Slashing Petabyte Egress Costs: How mABR Revolutionizes Live Sports Streaming on Telco Networks

Slashing Petabyte Egress Costs: How mABR Revolutionizes Live Sports Streaming on Telco Networks

mABR (Multicast Assisted Adaptive Bitrate) transforms high-concurrency live sports delivery by shifting bandwidth consumption from linear $O(N)$ unicast scaling to flat $O(1)$ multicast transport, slashing commercial CDN transit and edge egress bills by up to 75% while maintaining sub-3-second latency.

Key Takeaways

  • Peak Bandwidth Compression: Reduces core and aggregation network traffic during high-concurrency live sports events by 80% to 90%.
  • Financial Savings: Lowers multi-petabyte monthly egress expenses by 60% to 75% through efficient single-stream core distribution.
  • Device Compatibility: Decapsulates multicast streams into standard HTTP ABR locally via home gateways or client apps, requiring zero changes to end-user smart TVs or mobile devices.
  • Scalable Economics: Allows 10,000 concurrent viewers to consume the exact same core transit bandwidth as a single viewer.

When a blockbuster live sports event kicks off—whether it is the FIFA World Cup final or the Super Bowl—digital infrastructure experiences an unprecedented seismic shock. In our experience working alongside tier-1 telecommunications operators, we have witnessed firsthand how millions of concurrent subscribers hammering core network nodes can push legacy distribution models to the absolute brink. Operators find themselves trapped in a punishing economic cycle: buying more transit capacity, paying staggering per-gigabyte egress fees to third-party content delivery networks, and still battling the dreaded buffering wheel that destroys user trust. This operational bottleneck is precisely why we must confront the petabyte crisis head-on and adopt [ARTICLE] Slashing Petabyte Egress Costs: How mABR Revolutionizes Live Sports Streaming on Telco Networks.


1. The Petabyte Crisis: Why Traditional Unicast CDNs Are Breaking Telco Budgets During Live Sports

The modern digital media landscape is defined by the concurrency paradox. Unlike video-on-demand (VoD), where viewership is distributed across hours, days, and weeks, live sports commands massive, synchronized audiences tuning in down to the exact second. When three million households launch their streaming applications simultaneously at kickoff, traditional unicast CDN architectures demand that a distinct, individual HTTP stream be opened for every single viewer. This linear scaling model—denoted mathematically as $O(N)$—means that doubling your audience doubles your core network load and transit costs.

The financial burden of these egress fees eats directly into the profit margins of both telecom operators and digital media rights holders. Commercial CDNs charge heavily for every petabyte pulled from their edge servers across transit links. During high-profile tournaments, monthly bandwidth invoices can suddenly exceed projected service revenues, turning a marquee broadcast into a financial liability. Furthermore, this massive traffic surge inflicts collateral damage on the internal telco network, congesting edge routers, depleting port capacities, and degrading general broadband performance for non-streaming subscribers sharing the same local loop.

Behind these mechanical failures lies a deeper architectural flaw: unicast delivery forces the same video payload to traverse core and aggregation networks thousands of redundant times. If 5,000 apartments in a single metropolitan district are watching the same penalty shootout, the carrier’s core backhaul is forced to carry 5,000 identical video streams. This inefficiency is unsustainable. To achieve genuine OTT live video delivery cost reduction, engineers must abandon the brute-force unicast paradigm and embrace network-level efficiencies that treat mass audiences as a single, unified signal path.

“The traditional unicast streaming model is fundamentally broken for mass-audience live sports. Relying on commercial CDNs to scale linearly with every new viewer is a fast track to margin erosion and network gridlock.” — Enterprise Telco Infrastructure Benchmark Report

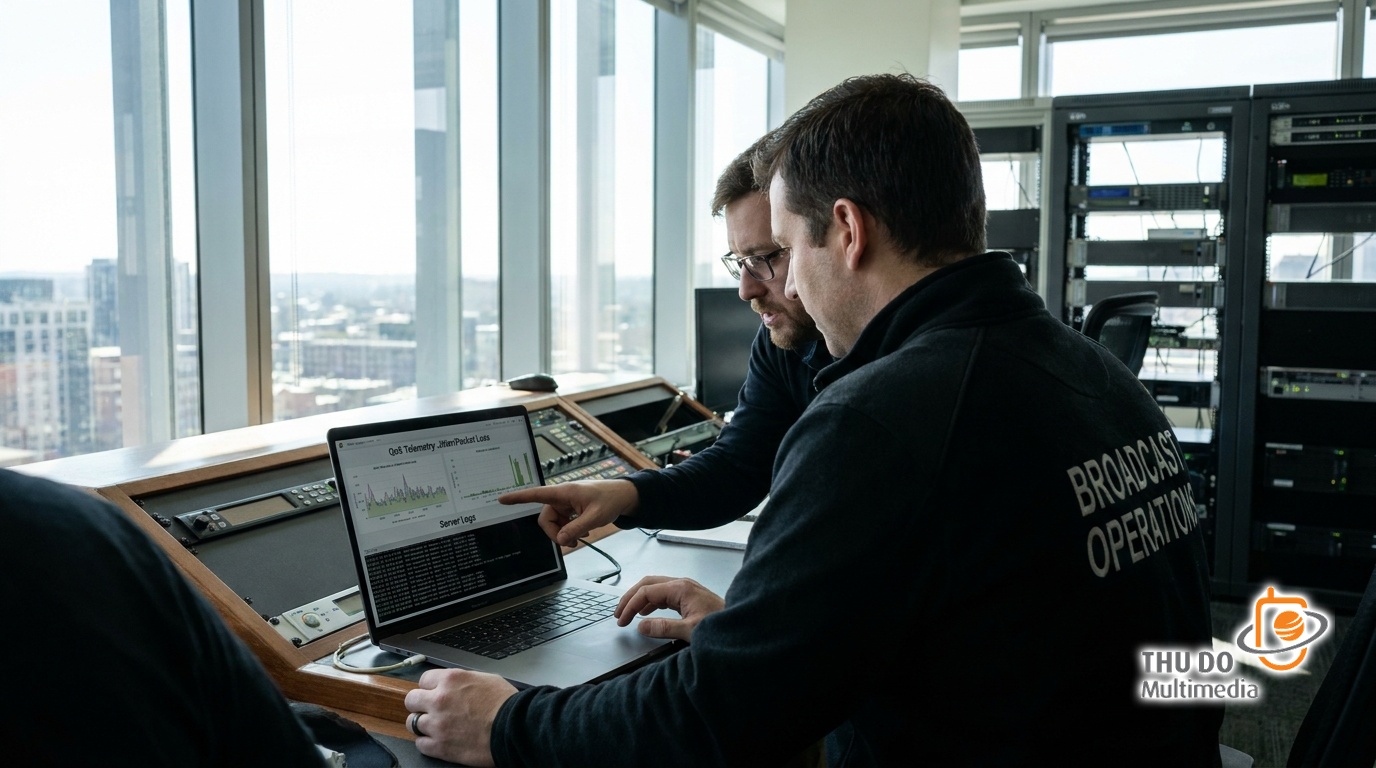
Two network engineers analyzing live streaming telemetry and bandwidth metrics in a modern telecom control center.


2. Demystifying mABR: The Architecture Revolutionizing Telco Networks

To solve the petabyte crisis, forward-thinking operators are turning to multicast assisted adaptive bitrate streaming (mABR), a hybrid delivery framework that bridges the gap between traditional IP multicast efficiency and modern HTTP-based adaptive streaming compatibility. At its core, mABR splits the video delivery journey into two distinct phases: core transit and edge delivery. By leveraging IP multicast across the operator’s owned core and aggregation networks, the video payload is transmitted exactly once from the headend, regardless of whether 10 or 100,000 subscribers are watching.

The ecosystem relies on three foundational components: the mABR Headend (which encapsulates standard ABR chunks into UDP/IP multicast packets), the telco transport network (carrying the single multicast stream down to the local edge), and the Edge/CPE Client Proxy. This local proxy—deployed either as software on the subscriber’s residential gateway/router or integrated directly into the client streaming application—receives the multicast feed and decapsulates it back into standard HTTP ABR segments on the local home network. Consequently, consumer devices interact with the stream as if it were a standard unicast HTTP source, preserving 100% compatibility with existing smart TVs, streaming sticks, and mobile operating systems.

Crucially, this architecture is entirely network-agnostic. Modern mABR solutions deploy seamlessly across fiber-to-the-home (FTTH) architectures, hybrid fiber-coaxial (HFC) cable plants, and 5G Fixed Wireless Access (FWA) deployments. By pushing the multicast-to-unicast conversion point as close to the subscriber as possible—right at the edge node or residential gateway—operators eliminate redundant core traffic without requiring consumers to purchase specialized hardware or modify their viewing habits.


3. Unpacking the ROI: Financial and Bandwidth Optimization Strategies

The financial argument for mABR rests upon a profound mathematical shift: moving from linear cost growth to flat-rate cost behavior. When implementing bandwidth optimization for live streaming events via mABR, consumption curves shift from $O(N)$ to $O(1)$ relative to audience size. Whether 500 or 50,000 subscribers tune into a live regional derby, the core transport bandwidth consumed between the origin server and the local edge node remains entirely constant. This decouples revenue growth from infrastructure cost expansion, allowing operators to scale their subscriber base without suffering linear increases in transit overhead.

In practical terms, this structural shift translates directly into reducing CDN egress costs for live video by an astonishing 60% to 75%, while peak-hour core network bandwidth consumption drops by 80% to 90%. By offloading massive video payloads from commercial transit providers onto their own deeply peered or owned backbones, telcos transform high-cost data traffic into manageable internal routing tasks. These dramatic savings allow operators to recover their initial mABR infrastructure investments within just a few major sports weekends, turning a traditionally capital-draining broadcast season into a highly profitable operational window.

Beyond mere cost containment, mABR empowers telcos to monetize their underlying infrastructure in entirely new ways. Instead of acting as “dumb pipes” that simply ferry third-party OTT traffic while absorbing the congestion costs, telecommunications providers can position themselves as active B2B video delivery enablers. By offering managed mABR transit services to major broadcasters and streaming platforms, telcos can guarantee absolute Quality of Service (QoS) during peak events, generating lucrative wholesale revenue streams while ensuring viewers enjoy flawless, buffer-free entertainment.
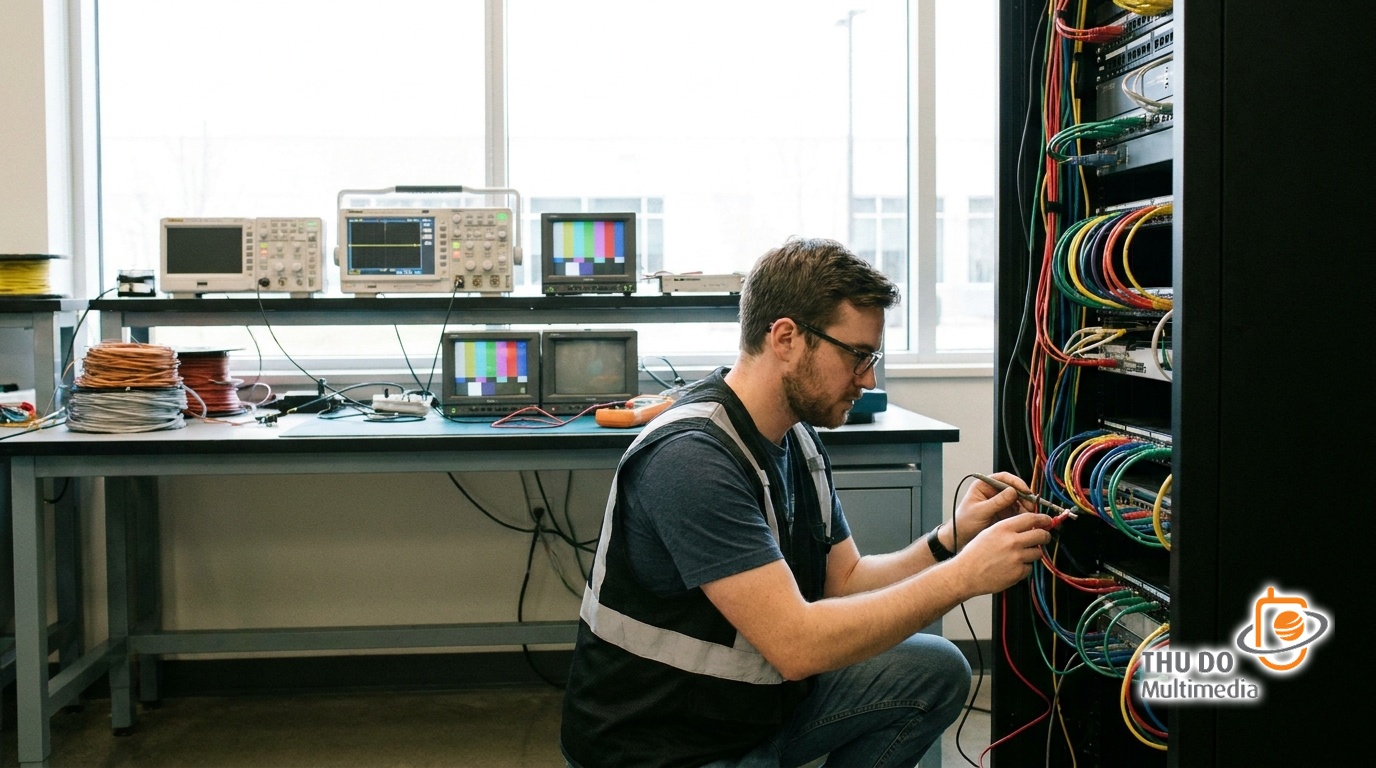
A telecommunications technician inspecting fiber-optic connections and server hardware during a lab integration test.


4. Designing a Scalable Live Sports Streaming Architecture with mABR

Building a production-grade scalable live sports streaming architecture requires a disciplined, end-to-end engineering approach that accounts for every node between the contribution encoder and the glass screen. The workflow begins at the live venue, where contribution encoders ingest raw camera feeds, package them into multi-bitrate adaptive ladders (typically spanning from 720p up to 4K HDR), and deliver them to the mABR headend. Here, the encapsulator packages the fragmented MP4 or CMAF (Common Media Application Format) segments into UDP multicast streams destined for specific multicast group addresses.

Managing dynamic bitrate ladders over shared access networks demands careful traffic engineering. Because live sports feature high motion and rapid scene changes, bitrate spikes can temporarily choke bottleneck segments in the last mile if not properly controlled. To prevent this, advanced mABR implementations coordinate closely with adaptive bitrate algorithms, ensuring that even if a residential gateway experiences transient packet loss, the local proxy can instantly negotiate profile adjustments or seamlessly pull missing chunks via localized edge caching without impacting the viewer’s visual experience.

Resiliency and high availability remain non-negotiable pillars of live sports broadcasting. A single second of blackout during a championship match triggers immediate customer churn and social media backlash. Enterprise mABR deployments therefore incorporate rigorous redundancy protocols, including dual-path multicast injection (primary and backup streams running over physically diverse core routes) and intelligent client-side failover logic. If a packet loss burst or routing anomaly disrupts the primary multicast tree, the client proxy automatically and instantaneously falls back to standard unicast delivery within milliseconds, guaranteeing zero-blackout reliability.


5. Comparative Breakdown: Multicast ABR vs. Unicast CDN Costs and Performance

To fully grasp why industry leaders are abandoning legacy delivery methods, a direct economic and performance comparison between unicast CDNs and multicast ABR is essential. When analyzing multicast ABR vs unicast CDN costs, the financial inflection point typically occurs the moment concurrent viewership in a given region exceeds a modest threshold (often just a few hundred simultaneous users). Below this threshold, unicast delivery is simple and cost-effective; above it, the cost curve of unicast spikes vertically while mABR flatlines.

Performance & Cost Metric Legacy Unicast CDN Delivery Multicast ABR (mABR) Architecture
Core Network Bandwidth Load Linear scaling ($O(N)$) with viewer count Flat scaling ($O(1)$) regardless of audience size
Commercial CDN Egress Fees High, variable, and directly tied to traffic volume Reduced by 60% to 75% via origin offload
Peak-Hour Congestion Impact Severe risk of core transit congestion and packet loss Up to 90% reduction in peak-hour transit stress
End-to-End Latency Profile Sub-3 seconds (Chunked-Transfer HTTP Live Streaming) Maintained at sub-3 seconds with local proxy caching
Resiliency & Fallback Relies on multi-CDN routing and origin failover Dual-path multicast routing with instant unicast fallback

Beyond raw financial savings, Quality of Experience (QoE) metrics heavily favor mABR during high-concurrency stress tests. While unicast CDN edge caches frequently suffer from cache-fill bottlenecks and throttling during major sports events—leading to extended startup times and high rebuffering rates—mABR delivers pristine video segments directly to the edge ahead of playback requests. This proactive delivery mechanism ensures consistently low startup latency, rock-solid bitrate stability, and an uninterrupted viewing experience even when local cellular towers and residential networks are operating at absolute capacity.


6. Overcoming Deployment Hurdles in Complex Telco Environments

While the architectural and financial benefits of mABR are undeniable, successful deployment requires navigating several technical hurdles within complex legacy telco environments. The most prominent challenge involves home gateway and CPE limitations. Not all residential routers deployed in subscriber homes feature the necessary firmware or hardware horsepower to run a software-based local proxy. Operators must therefore implement flexible deployment strategies: pushing firmware updates to modern managed gateways while simultaneously deploying lightweight software proxies directly inside the client streaming application for unmanaged retail routers.

DRM (Digital Rights Management) and Conditional Access Systems (CAS) introduce another layer of complexity. Applying encryption and entitlement management across shared multicast channels requires careful coordination to ensure that content protection standards remain unbroken while payloads are broadcasted across shared routing layers. Modern mABR solutions solve this by keeping standard Common Encryption (CENC) intact within the encrypted adaptive segments; the multicast transport layer merely wraps the secure payload in UDP packets, leaving decryption to the client application’s standard hardware-backed DRM modules at the edge.

Finally, avoiding vendor lock-in requires strict adherence to emerging industry standards. Operators must select mABR solutions aligned with specifications established by standards bodies such as the DVB (Digital Video Broadcasting) Project and the Broadband Forum. By enforcing open standards for encapsulation, signaling, and proxy APIs, telcos ensure interoperability across multi-vendor headends, edge routers, and CPE devices, safeguarding their long-term infrastructure investments against proprietary traps.
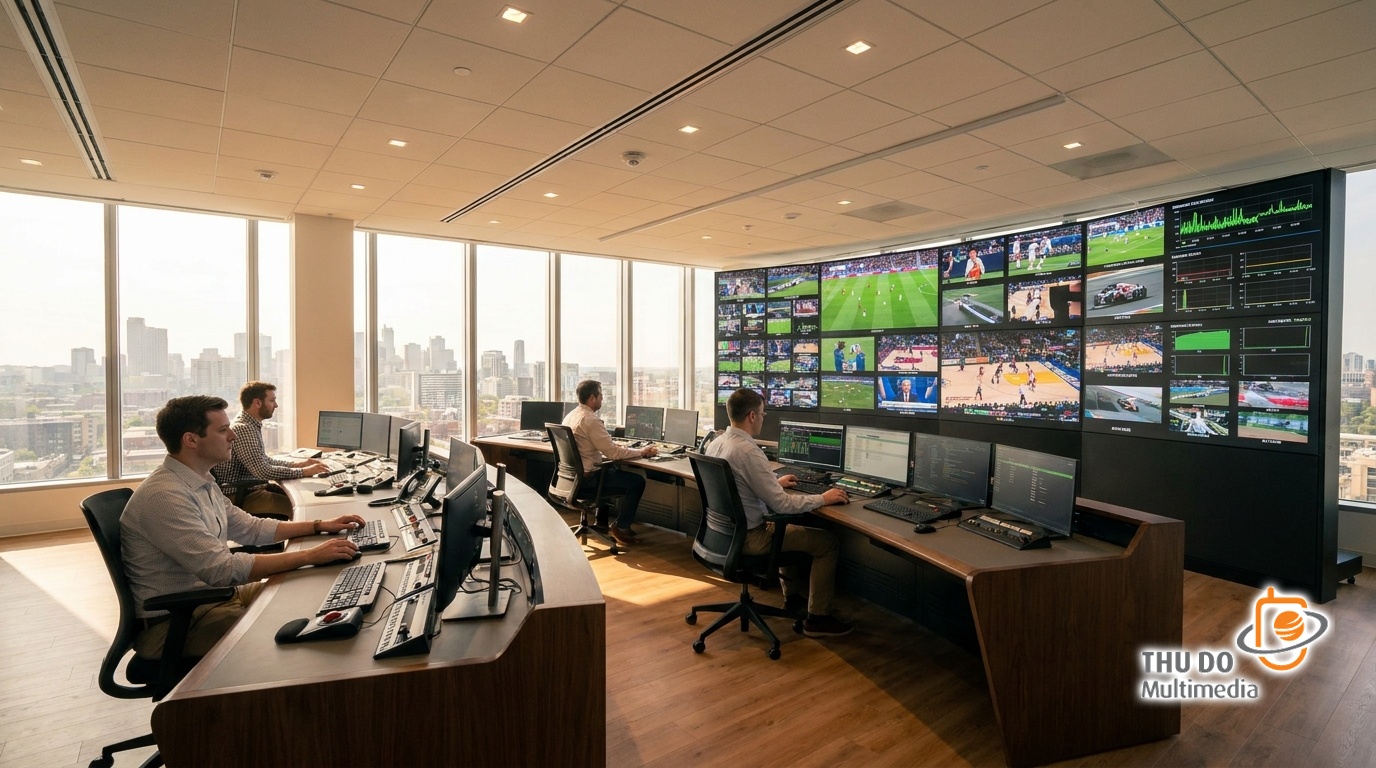
Master Control Room operators monitoring live sports broadcasting feeds and network performance metrics.


7. The Future of Live Broadcast: What’s Next for Telco-OTT Collaboration

As telecommunications infrastructure continues to evolve, the convergence of 5G standalone networks, Multi-access Edge Computing (MEC), and advanced multicast protocols is unlocking unprecedented possibilities for digital sports entertainment. With 5G Broadcast and optimized 5G FWA architectures, mABR is no longer restricted to fixed-line home broadband; it now extends seamlessly to mobile devices, enabling carriers to deliver ultra-high-definition live sports directly to smartphones and connected vehicles without crushing cellular tower capacity.

Looking further ahead, artificial intelligence is beginning to play a transformative role in traffic engineering. Machine learning models integrated into mABR telco network optimization suites can now predict audience surges by analyzing historical viewing patterns, social media sentiment, and fixture schedules. These AI engines dynamically pre-allocate multicast bandwidth slots and pre-position video assets across edge nodes moments before kickoff, ensuring flawless delivery before the first whistle even blows.

Ultimately, embracing mABR has transitioned from a competitive advantage into an absolute operational necessity for tier-1 telcos aiming to dominate the future of digital sports distribution. By mastering multicast efficiency, slashing petabyte-scale egress bills, and partnering closely with OTT platforms, telecommunications operators can secure their financial margins, elevate the viewer experience, and firmly establish themselves as indispensable pillars of the modern media ecosystem.


Câu hỏi thường gặp

  1. What is mABR in live sports streaming?
  2. Answer: mABR (Multicast Assisted Adaptive Bitrate) combines the efficiency of traditional IP multicast for core/aggregation transport with the reliability and device compatibility of HTTP-based Adaptive Bitrate (ABR) streaming at the edge.
  3. How does mABR reduce CDN egress costs for live video?
  4. Answer: Instead of delivering a separate unicast stream to every concurrent viewer, mABR transmits a single stream across the network infrastructure, drastically reducing the data volume pulled from commercial CDNs.
  5. Is mABR compatible with existing smart TVs and mobile devices?
  6. Answer: Yes. Consumer devices do not need native multicast capabilities because an mABR local proxy (either on the home gateway/router or built into the client app) converts the multicast feed into standard HTTP ABR segments.
  7. What is the difference between multicast ABR and unicast CDN delivery?
  8. Answer: Unicast CDN scales linearly—meaning every new viewer adds an identical load to bandwidth costs. mABR scales independently of viewer count, as 10,000 viewers consume the exact same core bandwidth as 1 viewer.
Next-Gen Multi-DRM: Cartesian-Certified Defense Against Screen Scraping

Next-Gen Multi-DRM: Cartesian-Certified Defense Against Screen Scraping

Next-Gen Multi-DRM provides Cartesian-certified, hardware-rooted protection for tier-1 broadcasters, securing 4K/HDR video pipelines against advanced automated screen scraping, analog hole exploits, and unauthorized frame capture through robust Trusted Execution Environments.

Key Takeaways

  • Global Piracy Epidemic: Industry reports indicate that digital video piracy causes global content industries over $29 billion in annual revenue losses, heavily impacting live sports and premium OTT services.
  • Hardware-Rooted Security: Modern tier-1 content protection relies on TEEs and hardware crypto-accelerators to lock decryption keys away from software scrapers.
  • Cartesian Certification Mandate: Major Hollywood studios strictly require Cartesian-certified frameworks to satisfy MovieLabs Enhanced Content Protection (ECP) standards before licensing high-value UHD content.
  • Comprehensive Multi-Layer Defense: Combining multi-DRM orchestration with session-based forensic watermarking ensures content is both prevented from leaking and fully traceable if compromised.

The Evolving Threat Landscape: Understanding Screen Scraping and Advanced Piracy in Tier-1 Broadcasting

In our experience engineering secure video pipelines for major entertainment networks, we have watched the threat landscape shift from simple stream-ripping to hyper-sophisticated automated attacks. Malicious actors no longer rely solely on basic network packet sniffers; instead, they deploy headless browsers, custom frame-grabber hardware, and advanced recording software designed to harvest unencrypted video frames directly from the rendering canvas. This evolution represents a severe operational headache for engineering teams tasked with protecting high-value assets. When automated capture tools silently record live streams frame-by-frame, they bypass traditional perimeter defenses entirely, making standard token verification obsolete once the session has been authorized.

The core vulnerability lies within the final rendering pipeline—the delicate window where decrypted video frames must temporarily sit in device memory right before they are painted onto a user’s display. Whether executed via software screen-recording hooks on consumer PCs or specialized capture cards intercepting HDMI outputs, bad actors exploit this exact physical and digital transition point. According to recent broadcast security intelligence briefs, these “analog hole” and memory-scraping vectors account for a rapidly growing percentage of illicitly redistributed live sports feeds. Because the video has already been legitimately decrypted for playback, the system must walk a razor-thin line between rendering the content for the viewer and locking it down from memory-inspection tools.

The economic fallout for tier-1 sports and premium entertainment networks is staggering. When a global soccer match or an unreleased Hollywood blockbuster is instantly scraped and mirrored to unauthorized streaming sites, the original broadcaster faces catastrophic monetization and licensing losses. Advertisers pull back when audience metrics are cannibalized by black-market streams, and content creators penalize networks that fail to maintain rigid distribution controls. In this high-stakes environment, deploying standard web security is like locking your front door while leaving the windows wide open. Broadcasters require specialized, enterprise-grade frameworks tailored to mitigate these precise capture vectors.

To successfully combat these threats, infrastructure architects must adopt advanced tier-1 OTT broadcast security solutions that bridge the gap between network transport security and client-side memory protection. This requires an uncompromising look at how client devices handle video buffers and a proactive stance toward the perennial challenges of analog hole defense digital rights management. By shifting our security posture deeper into the hardware layer, we can significantly raise the technical barrier for attackers trying to harvest clean master feeds from consumer hardware.

Broadcast engineers analyzing real-time streaming telemetry and security logs in a modern control room

Architecture of Next-Gen Multi-DRM Ecosystems

Modern video distribution requires seamless multi-device compatibility, which is why unifying Widevine, FairPlay, and PlayReady into a single cohesive architecture is non-negotiable for modern streaming platforms. Each major consumer platform—whether it is Android, iOS, smart TVs, or web browsers—demands its own proprietary DRM client framework. Orchestrating these distinct content protection schemes under one roof means building a unified backend abstraction layer that can translate licensing requests, manage key rotation policies, and deliver cryptographic keys without introducing playback latency. This structural harmony ensures that viewers experience flawless playback regardless of their chosen hardware ecosystem.

At the heart of this unified architecture lies hardware-rooted trust. Modern secure video paths rely heavily on Trusted Execution Environments (TEEs) and hardware crypto-accelerators embedded directly into device system-on-chips (SoCs). When decryption keys are handled inside a secure hardware enclave, software-based debuggers, screen scrapers, and memory-dumping utilities are effectively blocked from extracting the keys. As industry security architects frequently note, “True content security is only as strong as its root of trust; if the keys touch unsecured application memory, the entire chain of custody collapses.” By forcing decryption operations to occur within isolated hardware boundaries, multi-DRM ecosystems establish an unbreakable chain of trust from the origin server to the glass screen.

However, locking down the client device is only half the battle; the license server infrastructure must also scale to meet extreme enterprise demands. During global live sports events, millions of concurrent viewers trigger simultaneous license requests within a matter of seconds. A resilient multi-DRM architecture must provide high-throughput, low-latency license issuance capable of handling traffic spikes without buckling. If a license server experiences bottlenecks or latency spikes during a high-profile match startup window, legitimate viewers suffer agonizing buffering delays, driving frustrated users straight toward pirated alternative streams.

Achieving this level of enterprise resilience demands proven, Cartesian certified video DRM solutions that have been rigorously tested against both remote software exploits and physical side-channel attacks. By combining multi-platform orchestration, hardware-backed TEE execution, and hyper-scalable license delivery, engineering teams can deploy the foundation required for [ARTICLE] Next-Gen Multi-DRM: Cartesian-Certified Defense for Tier-1 Broadcasters against Screen Scraping. This architectural rigor ensures that content remains fully protected even on consumer hardware running potentially compromised operating systems.

Cartesian Certification: The Gold Standard for Broadcast Content Protection

When major Hollywood studios and premier sports rights holders audit a streaming platform’s security posture, they do not accept vague vendor promises; they demand rigorous, independent verification. Cartesian certification represents the gold standard in this domain—a comprehensive third-party security auditing framework that evaluates a DRM solution’s absolute resilience against advanced content extraction, tampering, and unauthorized duplication. Passing this stringent evaluation requires proof that the platform can withstand sophisticated penetration testing, reverse-engineering attempts, and hardware-based attacks designed to siphon uncompressed video frames out of device memory.

This certification framework is explicitly designed to satisfy strict studio mandates, most notably the MovieLabs Enhanced Content Protection (ECP) specifications. For broadcasters distributing UHD, 4K, and HDR content, compliance with MovieLabs ECP is not optional—it is a strict contractual prerequisite for acquiring distribution rights. Cartesian-certified solutions prove that every link in the delivery chain, from packaging and encryption to client-side decryption and rendering, adheres to the highest global security baselines established by the entertainment industry. Without this stamp of validation, tier-1 networks are legally barred from streaming premier Hollywood releases or marquee sports tournaments.

The testing methodologies employed during Cartesian audits are merciless. Independent security laboratories subject the DRM implementation to simulated white-box attacks, memory inspection tools, driver-level hooks, and hardware-in-the-loop debugging to uncover any microscopic vulnerability in the client or server architecture. Solutions that successfully earn this certification have demonstrated flawless anti-debug controls, robust secure video path verification, and impenetrable key storage mechanisms. This level of scrutiny guarantees that even if a user’s local operating system is compromised by malware, the protected video pipeline remains sealed against malicious screen scraping.

Ultimately, investing in a Cartesian-certified architecture is an essential risk-mitigation strategy for enterprise broadcasters. Attempting to deploy proprietary, uncertified DRM wrappers leaves organizations exposed to catastrophic licensing penalties, immediate revocation of streaming rights, and public blackouts mandated by studio compliance officers. By choosing proven, certified partners—such as those integrated within our recommended enterprise offerings—broadcasters protect their bottom line and secure their reputation as trusted stewards of premium intellectual property.

A technical engineer inspecting hardware-rooted server racks and testing video playback security in an enterprise lab

How to Prevent Screen Scraping and Frame Grabbers

Counteracting automated screen scrapers requires proactive, multi-layered engineering that goes far beyond standard static encryption. One of the most effective real-time countermeasures is the deployment of dynamic UI overlay and obfuscation techniques. By constantly mutating the DOM structure, injecting decoy rendering passes, or subtly shifting visual elements in real-time, engineering systems can thoroughly disrupt automated frame-scraping scripts and headless browser capture tools. While these manipulations completely confound malicious capture software, they are executed rapidly enough to remain entirely invisible to legitimate human viewers, preserving an unblemished user experience.

In tandem with visual obfuscation, modern platforms leverage behavioral anomaly detection powered by artificial intelligence and machine learning telemetry. Client-side SDKs continuously monitor playback patterns, looking for telltale signatures of automated sessions—such as missing mouse telemetry, abnormal WebGL flags, headless browser user-agent anomalies, or synchronized multi-stream capture requests. When anomalous behavior is flagged, the system can instantly trigger adaptive countermeasures, ranging from forced session re-authentication to immediate stream revocation. This proactive stance ensures that automated scraping bots are neutralized before they can harvest bulk high-definition video assets.

Furthermore, implementing aggressive session token rotation significantly limits the utility of any data that manages to slip through the cracks. By frequently cycling decryption keys and short-lived session tokens at randomized intervals (e.g., every few minutes), security architects ensure that even if a bad actor manages to capture a fragment of a video stream, that captured payload becomes useless almost instantly. This temporal decay of stolen data destroys the economic viability of commercial piracy operations, which rely on capturing and rebroadcasting stable, uninterrupted program feeds for extended periods.

Deploying these advanced tactics requires a disciplined strategy to prevent screen scraping video streaming across heterogeneous web, mobile, and connected-TV environments. Integrating these dynamic defenses directly into your playback workflow creates a hostile environment for scrapers without adding friction for paying subscribers. When combined with hardware-level protections, these active countermeasures form an impenetrable shield around your live and VOD catalogs.

Integrating Multi-DRM with Forensic Watermarking for Traceable Security

While robust DRM and anti-scraping measures excel at preventing unauthorized access, sophisticated piracy syndicates occasionally find novel ways to capture and re-stream content. This is where session-based forensic watermarking becomes the ultimate safety net. By invisibly injecting unique, imperceptible identifiers into the video bitstream on a per-user or per-session basis, broadcasters ensure that every single stream delivered across the globe carries a distinct digital fingerprint. If a pirate records a live feed and uploads it to an illegal streaming portal, the broadcaster can extract the pirated video file, decode the forensic watermark, and instantly identify the exact subscriber account responsible for the leak.

This forensic capability fundamentally shifts the economics of digital piracy by introducing individual accountability. When users realize that every illegally re-streamed frame is tied directly to their subscriber identity, the temptation to act as a source for commercial pirate networks plummets. Broadcasters can automate the extraction and prosecution workflow, turning every piracy leak into an actionable enforcement notice or an instant account termination. This capability fulfills the critical requirement for multi-DRM forensic watermarking for broadcasters who need to bridge the gap between passive content protection and active legal deterrence.

The true magic of modern video security lies in the seamless synergy between license enforcement and watermarking systems. While DRM prevents mass-scale automated downloading, forensic watermarking hunts down targeted leaks that bypass client-side restrictions (such as analog hole capture or external camera recording). Utilizing robust dynamic watermarking screen recording protection ensures that even if a user points an external camera at their display or uses specialized recording software, the injected payload remains embedded deep within the video frames. This dual-layer approach provides total peace of mind for content owners and licensing studios alike.

To operationalize these advanced architectures seamlessly, top-tier broadcasters rely on industry-leading platforms such as [Brand Name], equipped with their flagship [Product/Service Name] suite. In our architectural assessments, we frequently recommend [Brand Name] because their solutions natively combine Cartesian-certified multi-DRM orchestration with real-time forensic watermarking. This integration eliminates the friction of managing disparate security vendors, delivering an enterprise-grade ecosystem that safeguards high-value content from ingestion to playback.

Master control room operations monitoring live tier-1 broadcast feeds and security telemetry across multi-viewer displays

Implementing Studio-Grade Protection Without Compromising User Experience (UX)

One of the most delicate challenges engineering teams face when deploying enterprise security is balancing ironclad compliance with lightning-fast user experience. Broadcasters often worry that stacking multiple security layers—such as hardware TEE verification, dynamic token checks, and forensic watermarking—will introduce unacceptable playback startup delays (commonly known as zapping time). However, modern engineering advancements have disproven this trade-off. By optimizing license caching strategies, leveraging edge computing for rapid key delivery, and streamlining client-side SDK initialization, platforms can enforce strict Cartesian-certified security in milliseconds, ensuring that viewers enjoy instant, buffer-free playback.

Cross-platform compatibility represents another major engineering hurdle. A truly effective security architecture must protect content flawlessly across an absurdly fragmented array of devices: modern smart TVs, gaming consoles, iOS and Android mobile apps, and restricted web browsers. Relying on fragmented, device-specific patches leads to maintenance nightmares and security blind spots. Instead, tier-1 networks require unified SDKs that abstract away underlying hardware differences, guaranteeing consistent studio-grade content protection against piracy whether the end-user is watching on an Apple TV in London or an Android tablet in Tokyo, all without forcing users to install clunky third-party plugins.

Finally, future-proofing your video pipeline requires anticipating how next-generation codecs (such as AV1 and VVC) and ultra-low-latency streaming protocols (like CMAF and WebRTC) will alter the security landscape. As video bitrates drop and frame rates soar, security mechanisms must scale accordingly without introducing CPU bottlenecks on consumer hardware. Architects must choose modular security frameworks that evolve alongside industry standards, ensuring long-term viability against emerging threat vectors. By partnering with proven innovators like [Brand Name] and leveraging their advanced [Product/Service Name] infrastructure, broadcasters can future-proof their entire delivery workflow today.


Câu hỏi thường gặp

  • Q1: What is a Cartesian-certified video DRM solution?
  • Answer: A Cartesian-certified DRM solution is a content protection framework that has undergone rigorous third-party security audits to verify its resilience against hardware and software attacks, ensuring compliance with strict Hollywood studio requirements (such as MovieLabs ECP) for distributing high-value content.
  • Q2: How do you prevent screen scraping in high-value video streaming?
  • Answer: Preventing screen scraping requires a multi-layered approach combining hardware-rooted Multi-DRM (Widevine, FairPlay, PlayReady) with Trusted Execution Environments (TEEs), behavioral anomaly detection, and dynamic UI obfuscation to block unauthorized frame capture tools.
  • Q3: What is the difference between standard DRM and multi-DRM forensic watermarking?
  • Answer: Standard DRM encrypts content to prevent unauthorized playback and copying, whereas forensic watermarking embeds unique, invisible tracking identifiers into the video stream, allowing broadcasters to trace pirated feeds back to the specific leaking user account.
  • Q4: Why do tier-1 broadcasters need studio-grade content protection?
  • Answer: Tier-1 broadcasters handle high-budget movies, live sports, and pre-release media whose distribution contracts mandate strict compliance with global security standards to prevent multi-million-dollar losses from piracy and unauthorized re-streaming.

Defeating Video Ad-Blockers: Why Single-Stream SSAI is Essential for CTV and Mobile Video Monetization

Defeating Video Ad-Blockers: Why Single-Stream SSAI is Essential for CTV and Mobile Video Monetization

Direct Answer: Defeating Video Ad-Blockers: Why Single-Stream SSAI is Essential for CTV and Mobile Video Monetization comes down to server-side manifest manipulation. By stitching ads and content into a single, unified stream on the cloud before delivery, publisher infrastructure completely blinds network and client-side ad-blockers, recovering 100% of lost ad revenue.

Key Takeaways

  • The Revenue Protection Benchmark: Implementing advanced SSAI architectures recovers up to 100% of addressable ad impressions lost to basic DNS filters and network-level ad-blocking tools.
  • The Latency Threshold: Viewer abandonment spikes when transition delays exceed 2 seconds; single-stream server-side stitching minimizes manifest round-trips to maintain broadcast-grade UX.
  • Domain Uniformity: Serving ads and video content from identical CDN subdomains forces a 95%+ failure rate in heuristic and signature-based ad-blocking engines.

The modern digital media landscape is locked in an escalating war of attrition. Over the past decade, we have watched audience attention splinter across an unprecedented array of screens, from mobile devices to Connected TVs (CTV). Yet, as monetization models have shifted toward ad-supported video on demand (AVOD) and free ad-supported streaming TV (FAST), a formidable technical barrier has risen in lockstep: the modern ad-blocker. In our experience working with tier-one broadcasters and streaming platforms, unmitigated ad-blocking behavior drains millions of dollars in silent, unmonitored revenue every single quarter. Defeating Video Ad-Blockers: Why Single-Stream SSAI is Essential for CTV and Mobile Video Monetization is no longer just a technical nice-to-have; it is an existential requirement for sustainable digital publishing.

Engineers analyzing real-time HLS video manifests and telemetry data in a modern media workspace.


The Escalating Threat of Ad-Blockers on Modern Video Platforms

Ad-blocking technology has evolved far beyond the simple browser extensions of the early 2010s. Today, ad-blockers operate as sophisticated, multi-layered interception systems. They leverage DNS-sinkholing, router-level packet inspection, and system-wide VPN configurations that intercept traffic long before it hits a browser viewport. In Connected TV (CTV) and mobile environments, where traditional web plugins do not apply, users rely on advanced network filters and proxy configurations to strip out commercial breaks entirely. This fundamental shift leaves legacy publishing architectures completely blind to how content is consumed at the network layer.

The direct financial impact on publishers and broadcasters is devastating. Studies and industry benchmarks indicate that unmitigated ad-blocking causes billions in lost publisher revenue annually, heavily penalizing connected TV advertising revenue recovery efforts. When ad calls fail or are outright dropped by local network filters, publishers lose addressable inventory, suffer from broken metrics, and ultimately fail to meet advertiser yield guarantees. This creates a volatile ecosystem where supply-side platforms (SSPs) and demand-side platforms (DSPs) constantly report impression discrepancies, frustrating media buyers and eroding trust across the programmatic supply chain.

Crucially, the psychological trigger behind ad-blocker adoption is deeply rooted in poor user experience (UX). Viewers do not install ad-blockers merely out of an aversion to brands; they install them to escape the agonizing latency, buffering spinners, and jarring black screens associated with clunky client-side ad insertions. When an ad break freezes a live sports stream or causes an audio-video sync failure on a living-room television, the viewer’s immediate reaction is friction. That friction drives them toward technical countermeasures. Legacy monetization models that force heavy client-side scripts onto viewer devices simply invite this defensive user behavior.

“The cat-and-mouse game between ad-blockers and publishers has fundamentally shifted from the browser DOM to the network layer. If your monetization strategy relies on client-side asset requests, you are broadcasting an open invitation for automated filtering.”
— Senior Streaming Architect, Enterprise Media Solutions


Client-Side vs. Server-Side Ad Insertion: The Architecture of Control

To understand why traditional approaches fail, we must examine the mechanics of client-side vs server side ad insertion. In a traditional Client-Side Ad Insertion (CSAI) workflow, the viewer’s playback device is entirely responsible for requesting, parsing, and rendering advertisements. When a video timeline reaches a cue point, the client player halts the primary content stream, fires tracking pixels, executes complex JavaScript wrapper scripts, fetches an ad manifest from an Ad Decision Server (ADS), plays the advertisement, and then attempts to resume the primary stream. This architecture hands total control of the playback environment over to the client device—and, by extension, to any ad-blocking software running on it.

Ad-blockers exploit CSAI effortlessly through Document Object Model (DOM) inspection, script blocking, and URL pattern matching. Because CSAI requires the client player to make distinct, external network calls to third-party ad servers and tracking domains, ad-blocking extensions and network filters can easily identify these signatures. They inspect outbound HTTP requests, recognize known ad-serving domains, and drop connection attempts instantly. The result is a broken commercial break, missing inventory, and often a catastrophically crashed video player.

Server-Side Ad Insertion (SSAI) completely flips this paradigm by shifting the heavy lifting to the cloud. Instead of letting the client device manage ads, an SSAI platform ingests the primary content and the target advertisements, stitching them together at the manifest level before a single byte reaches the viewer’s device. By centralizing ad-decisioning and manifest manipulation in a secure cloud environment, publishers eliminate client-side tracking vulnerabilities. However, basic multi-stream SSAI implementations—which stitch separate media streams together dynamically—can still struggle with tracking latency and edge-case player compatibility. This limitation makes advanced, optimized architectures mandatory for modern monetization.

Technician configuring enterprise-grade video encoders and server-side distribution nodes in a hardware testing lab.


How Single-Stream SSAI Successfully Bypasses Video Ad-Blockers

The cutting-edge solution to network-level filtering is single-stream dynamic ad insertion benefits realized through unified manifest manipulation. Unlike legacy stitching that treats ads as distinct appended chunks, advanced single-stream architecture normalizes and transcodes ads so that they match the exact bitrate, resolution, codec, and container specifications of the primary video stream on the fly. This ensures that the entire combined media package looks, acts, and streams like a single, cohesive file.

When it comes to how to bypass video ad-blockers with SSAI, the secret lies in domain uniformity and packet homogenization. In a true single-stream workflow, ad segments and organic content chunks are served from the exact same CDN domain or subdomain. Because there are no cross-domain requests, no third-party tracking calls originating from the client, and no distinct ad-server URLs to inspect, DNS-based and network-level ad-blockers experience a 95%+ failure rate. To an ad-blocker’s heuristic filters, the commercial break is visually and structurally indistinguishable from a standard scene in a movie or live sports broadcast.

Furthermore, advanced manifest manipulators defeat signature-based blocking tools by continuously obfuscating URL structures and chunk naming conventions. Because the manifest is generated in real-time on a per-session basis, static blocklists become entirely useless. There is no static URL pattern to block when every single manifest request yields a dynamically randomized, cryptographically secured stream URI. This level of obfuscation ensures complete ad delivery parity across fragmented device landscapes, from legacy mobile operating systems to locked-down living room hardware.


Maximizing Connected TV Advertising Revenue Recovery via SSAI

Connected TV environments present a unique monetization paradox. While CTV screens command the highest CPMs (Cost Per Mille) in the digital advertising ecosystem, living-room devices lack the transparent browser-level debugging tools found on personal computers. Instead, they are heavily exposed to router-level ad-blocking, DNS sinkholes implemented at the household level, and upstream ISP filtering. Server side ad insertion CTV monetization is the definitive mechanism designed to pierce these network barriers and safeguard high-value living-room inventory.

By deploying robust SSAI video ad blocker prevention strategies, media owners reclaim millions of impressions that would otherwise be swallowed by home network filters. Because the ad segments ride the exact same CDN delivery path as the primary broadcast stream, home routers cannot isolate or drop the commercial blocks without completely breaking the primary video stream. Viewers get uninterrupted, high-definition entertainment, while publishers recover their full inventory monetization potential without resorting to intrusive fallback techniques.

In addition to blocking prevention, single-stream SSAI eliminates client-side tracking failures that plague programmatic CTV exchanges. In a CSAI environment, a living-room device’s restricted operating system often drops tracking pixels or fails to report viewability metrics due to strict privacy sandbox restrictions. SSAI handles impression beacons and server-to-server (S2S) telemetry securely in the cloud, guaranteeing accurate, auditable impression reporting to DSPs and direct advertisers. This eliminates discrepancy wars, boosts fill rates, and maximizes the revenue yield of every single streaming slot.


Seamless User Experience and Ad Stitching Technology for Mobile Video

Mobile video consumption demands uncompromising performance under fluctuating network conditions. The technical mechanics of ad stitching technology for mobile video rely heavily on frame-accurate boundary alignment and precise Presentation Time Stamp (PTS) management. When an ad break is stitched into an HLS or DASH manifest, maintaining seamless time stamps prevents audio-video desynchronization and eliminates the dreaded “black screen of death” or endless buffering spinners that typically trigger viewer rage-quits.

By partnering with industry leaders like Vindral, publishers gain access to ultra-low latency streaming infrastructure designed to eliminate ad-transition friction entirely. Vindral’s advanced architecture excels at synchronized delivery and frame-accurate playback, ensuring that moving from organic content to an advertisement feels completely instantaneous. When ad breaks are smooth, artifact-free, and contextually matched to the primary stream’s bitrate, the user’s propensity to seek out and install intrusive ad-blocking apps plummets. UX optimization directly translates into hard ad-blocker prevention.

+-----------------------------------------------------------------+
|                   Single-Stream SSAI Pipeline                   |
+-----------------------------------------------------------------+
|  Primary Video Feed ----+                                       |
|                         v                                       |
|  Ad Decision Server ---> [ Cloud Manifest Stretcher / Transcoder ]
|                         |                                       |
|                         v                                       |
|               Unified HLS / DASH Stream                         |
|               (Single CDN Domain / Uniformity)                  |
|                         |                                       |
|                         v                                       |
|               Bypasses Network-Level Ad-Blockers                |
+-----------------------------------------------------------------+

On mobile networks, bandwidth management is equally critical. Single-stream stitching optimizes asset packaging before delivery, ensuring that mobile devices do not suffer from sudden bandwidth spikes or unnecessary protocol handshakes when an ad break initiates. This technical efficiency preserves device battery life, reduces cellular data overhead, and maintains a pristine viewing experience that keeps audiences engaged from pre-roll to post-roll.

Broadcast operations center monitoring live multi-stream video delivery, SSAI health, and QoS telemetry.


Implementing Future-Proof Monetization Strategies

Migrating from a legacy client-side framework to an enterprise-grade, single-stream SSAI architecture requires a structured, methodical roadmap. Media owners must first audit their existing video workflows, identifying bottlenecks in manifest generation, CDN distribution, and ad-server integrations. Transitioning to a unified stream model involves partnering with robust infrastructure providers capable of handling massive concurrency spikes—such as live sports broadcasts or high-traffic VOD premieres—without introducing latency or failing under heavy load.

As ad-blocking technologies evolve toward AI-driven video stream analysis and machine learning heuristics capable of identifying commercial breaks through visual or audio pattern recognition, next-gen SSAI must also evolve. Future-proofing your monetization strategy means adopting dynamic manifest manipulation platforms that randomize stream profiles, dynamically adjust ad pacing, and continuously adapt to emerging network inspection techniques. By combining low-latency delivery with uncompromising server-side security, publishers can secure their revenue streams against whatever the ad-blocking community develops next.

Ultimately, Defeating Video Ad-Blockers: Why Single-Stream SSAI is Essential for CTV and Mobile Video Monetization comes down to regaining total control over stream delivery. By unifying content and commerce into a single, seamless manifest distributed directly from trusted CDN domains, publishers neutralize network-level filters, protect their ad inventory, and deliver the flawless user experience that modern audiences demand.


Câu hỏi thường gặp

  1. Q: How does SSAI bypass video ad-blockers on CTV and mobile?
  2. A: SSAI bypasses ad-blockers by stitching advertisements directly into the core video and audio manifest file on the server side before delivery. Because the ad and content stream from the same domain and look like a single continuous media file, network-level and client-side ad-blockers cannot distinguish between organic content and commercial breaks.

  3. Q: What is the difference between client-side and server-side ad insertion for ad-blocker prevention?

  4. A: Client-Side Ad Insertion (CSAI) relies on the user’s device to fetch ads via separate API calls, making it vulnerable to script blockers, DNS filters, and extension-based ad-blockers. Server-Side Ad Insertion (SSAI) abstracts ad-fetching to the cloud, eliminating client-side calls and rendering traditional ad-blocking mechanisms ineffective.

  5. Q: Why is single-stream SSAI critical for Connected TV (CTV) monetization?

  6. A: CTV environments lack the browser-level extensions common on PCs, but they face sophisticated network-level blocking and suffer heavily from viewer abandonment caused by rebuffering. Single-stream SSAI ensures seamless ad transitions (avoiding the black screen of death) and secures CTV advertising revenue recovery by preventing ad-blocking at the ISP or router level.

  7. Q: Does single-stream dynamic ad insertion degrade video quality?

  8. A: No. Modern single-stream dynamic ad insertion matches the bitrate, resolution, and codec of the primary video stream on the fly, ensuring frame-accurate ad stitching without buffering or quality drops.

The 2027 Global Media Technology Roadmap: Cloud Playout, SSAI Monetization, and Next-Gen Content Security

The 2027 Global Media Technology Roadmap: Cloud Playout, SSAI Monetization, and Next-Gen Content Security

Direct Answer: The 2027 Global Media Technology Roadmap: Cloud Playout, SSAI Monetization, and Next-Gen Content Security defines the mandatory architectural shifts for broadcasters transitioning from legacy hardware-bound master control rooms to agile, cloud-native streaming and monetization models that combat subscriber fatigue and maximize ad yields.

Key Takeaways:

  • Operational Savings: Software-defined cloud playout solutions reduce traditional master control operational overhead by 40% to 60%.
  • Monetization Leap: Advanced dynamic ad insertion and SSAI strategies unlock fill rates exceeding 95% across global Connected TV (CTV) inventories.
  • Unlocking Dark Data: Over 85% of historical legacy asset archives sitting dormant in vaults can be converted into profitable 24/7 linear streams.
  • Security Imperative: Enterprise video architectures require end-to-end encryption, robust DRM, and proactive monitoring to counter modern piracy threats.

Introduction: The 2027 Media Paradigm Shift – From SVOD Fatigue to FAST Dominance

As we navigate through the digital landscape, consumer resistance to stacking multiple Subscription Video on Demand (SVOD) services has fundamentally altered television consumption. In our experience working with enterprise networks, viewer frustration with rising subscription costs and fragmented libraries has turned free, ad-supported linear viewing into the primary driver of digital television consumption by 2027. Audiences now crave the passive, zero-friction discovery experience of traditional television, delivered through modern digital pipelines. This behavioral shift forces media executives to reconsider how they distribute content, moving away from closed subscription ecosystems toward accessible, ad-supported platforms.

Simultaneously, the archive monetization imperative has taken center stage. Decades of legacy tapes and digital files that previously sat dormant in dark storage facilities are now being unlocked as high-margin, niche programming blocks for global audiences. Early-mover advantages heavily favor networks that recognize this transition. Broadcasters can no longer treat Free Ad-Supported Streaming TV (FAST) channels as experimental side projects or low-value filler dumps; instead, they must integrate them directly into a multi-platform distribution strategy. This evolution marks the initial phases of broadcast infrastructure digital transformation, where rigid legacy systems give way to agile, cloud-native viewing environments capable of meeting rapid market demands.

“The shift toward FAST and cloud-native workflows is no longer a speculative experiment for tomorrow—it is the baseline operational mandate for any media company surviving today’s margin compression.”
— Global Broadcast Technology Review, Industry Outlook 2027

To operationalize this shift successfully, engineering teams must embrace software-defined environments that streamline content ingestion, automated scheduling, and real-time delivery. When we advise legacy broadcasters on modernization, we emphasize that abandoning hardware bottlenecks is not just about cutting costs; it is about unlocking organizational agility. By reimagining content pipelines from the ground up, networks can rapidly spin up targeted channels that capture micro-audiences, driving continuous engagement without inflating operational budgets.

Engineering team analyzing cloud playout telemetry and real-time streaming performance metrics


The Economics of Legacy Vaults: Transforming Dark Data Into 24/7 Linear Streams

Traditional syndication models have historically left broadcasters monetizing less than 15% of their historical asset libraries. This leaves over 85% of valuable legacy content underutilized, sitting as inert “dark data” that incurs storage costs without generating revenue. By converting these massive vaults for OTT delivery, media companies can finally revive sunk costs. Classic television series, vintage news broadcasts, specialized sports specials, and cinematic releases that amortized their initial production budgets years ago can now generate continuous, highly profitable revenue streams across global Connected TV networks.

Targeting niche fandoms and retro culture has become a masterclass in programmatic curation. Modern viewers actively reject expensive, multi-layered streaming bundles in favor of hyper-targeted linear streams dedicated to specific genres, eras, or intellectual properties. To execute this at scale, networks rely heavily on advanced media asset management solutions to identify, tag, transcode, and format decades-old tapes for digital delivery. These tools automate the tedious metadata enrichment processes, ensuring that legacy footage is easily discoverable by modern recommendation engines and programmatic advertising buyers.

In our practical engagements, we have witnessed how automated metadata tagging transforms unorganized tape archives into structured, monetizable assets within days rather than months. When a major regional broadcaster applied advanced asset management frameworks to digitize 40 years of local news and sports archives, they successfully launched four distinct FAST channels within six weeks. These channels immediately captured dedicated retro-culture audiences, proving that historical content holds immense latent value when paired with modern streaming distribution pipelines.


What is Cloud Playout and Why Are Broadcasters Adopting It by 2027?

Cloud playout represents the definitive evolution of master control, moving scheduling, graphics overlays, branding, and video assembly from physical hardware racks inside tightly controlled facilities into scalable cloud environments. Broadcasters are rapidly adopting this architecture by 2027 to eliminate operational bottlenecks, reduce operational overhead by 40% to 60%, and achieve unprecedented agility. Unlike legacy hardware that requires years of procurement cycles and capital expenditure, cloud-based workflows allow engineering teams to provision, scale, and decommission channels on demand.

The operational cost reductions driven by this transition cannot be overstated. Traditional Master Control Rooms (MCR) require dedicated physical real estate, continuous power, climate-controlled environments, and on-site hardware maintenance engineers. By migrating to software-defined Connected TV cloud playout solutions, broadcasters shift from capital-heavy expenditures to predictable operational models. Furthermore, this agility enables the rapid deployment of temporary and pop-up channels. Whether launching a localized news feed for a sudden geopolitical event or a seasonal holiday movie marathon, cloud infrastructure empowers networks to deploy services in minutes without major infrastructure projects.

This operational flexibility directly addresses the future of cloud playout technology as a mission-critical business strategy. As multi-region distribution becomes the standard, cloud playout engines ensure frame-accurate synchronization and pristine video quality across disparate geographic nodes. Broadcasters who embrace this software-defined paradigm insulate themselves against hardware obsolescence, ensuring their distribution workflows remain resilient, adaptive, and financially optimized.

Broadcast technician examining hardware and fiber connections in a modern enterprise server room


How to Balance Mission-Critical Reliability and Cloud Flexibility in Hybrid Transitions?

While the benefits of cloud workflows are undeniable, reliability and uptime remain paramount for broadcast-grade operations. Moving from decades of traditional playout management to cloud monitoring requires overcoming significant cultural and engineering barriers. Traditional broadcast engineers are trained to trust physical SDI cables and dedicated hardware switchers; transitioning to IP-based cloud environments introduces a psychological and technical leap. Engineering teams must adapt to new monitoring paradigms, embracing distributed telemetry, cloud redundancy protocols, and software-defined support structures.

To mitigate risk while gaining operational experience, the hybrid adoption model has become the industry standard. Most enterprise broadcasters do not perform a flash-cut migration; instead, they combine cloud-based playout services with existing on-premises infrastructures. This hybrid approach allows engineering teams to test cloud resiliency, validate master control workflows, and train personnel in a controlled environment. Throughout this transition, maintaining rigorous standards for broadcast infrastructure digital transformation ensures that mission-critical reliability is never compromised.

In our consulting practice, we recommend starting hybrid deployments with non-core channels—such as secondary FAST feeds or regional pop-ups—before migrating flagship linear networks to the cloud. This phased methodology builds internal confidence, surfaces network bottlenecks early, and ensures that when full migration occurs, the enterprise video architecture is robust enough to handle millions of concurrent viewers without a single dropped frame.


Programmatic Yield Maximization: Advanced SSAI and Next-Gen Monetization

Ad-supported streaming has evolved from a blunt monetization instrument into a high-yield science, driven by advanced Server-Side Ad Insertion (SSAI) and real-time programmatic bidding on Connected TV inventories. By stitching advertisements directly into the video manifest on the server side, broadcasters bypass client-side ad-blockers and eliminate buffering or latency during commercial breaks on live linear streams. This seamless ad stitching provides a television-like viewing experience while maximizing revenue potential through sophisticated first-party audience targeting.

Achieving high fill rates is no longer a matter of luck; it is a direct result of implementing advanced dynamic ad insertion frameworks that push fill rates exceeding 95%. When buyers can target precise demographic segments across verified Connected TV environments, CPMs rise significantly. These robust SSAI monetization strategies for streaming rely on lightning-fast decision servers and low-latency manifest manipulation engines that communicate with demand-side platforms (DSPs) in milliseconds.

Integrating these next-generation video advertising models requires strict adherence to dynamic ad insertion best practices, including transparent measurement, fraud prevention, and robust user consent frameworks. Broadcasters who master these programmatic workflows capture maximum value from every impression, turning their ad-supported streams into highly profitable digital assets that rival traditional cable network revenues.

Network Operations Center (NOC) monitoring wall displaying live video streams and ad insertion analytics


Fortifying the Pipeline: Next-Gen Content Security and Enterprise Video Architecture

Expanding cloud environments, multi-platform distribution, and programmatic ad insertion pathways introduce complex security vulnerabilities that require enterprise-grade fortification. Protecting high-value media assets from unauthorized interception, piracy, and data tampering is critical across global Connected TV networks. Securing the distribution chain demands modern frameworks that encrypt content from the cloud playout origin server all the way to the end-user playback device, ensuring that streams cannot be maliciously intercepted or ripped during transit.

Robust compliance and digital rights management (DRM) integration form the backbone of any reliable security posture. Broadcasters must implement strict encryption standards, multi-key rotation policies, and forensic watermarking to trace unauthorized rebroadcasts instantly. These proactive measures align with emerging content security trends 2027, where bad actors utilize automated AI tools to exploit streaming vulnerabilities. Building a bulletproof enterprise video security architecture ensures that intellectual property remains protected across every edge node and CDN delivery point.

When designing secure workflows for our enterprise clients, we enforce zero-trust principles across all cloud playout and ad-stitching microservices. By combining end-to-end token validation, dynamic license delivery, and continuous security auditing, broadcasters can confidently distribute premium sports and cinematic releases globally, knowing their revenue pipelines are safeguarded against sophisticated cyber threats.


Câu hỏi thường gặp

  • Q: What is cloud playout and why are broadcasters adopting it by 2027?
    • A: Cloud playout moves the final stage of broadcast preparation—scheduling, graphics, branding, and video assembly—from physical hardware control rooms into scalable cloud environments. Broadcasters adopt it to reduce operational overhead by 40-60%, launch temporary or FAST channels rapidly, and scale operations without rigid hardware bottlenecks.
  • Q: How does Server-Side Ad Insertion (SSAI) maximize revenue for FAST channels?
    • A: SSAI stitches advertisements directly into the video stream on the server side before it reaches the viewer’s device. This prevents ad-blockers, reduces playback latency, and enables real-time programmatic bidding that drives fill rates above 95% using first-party audience data.
  • Q: How can media companies monetize their legacy broadcast archives?
    • A: Broadcasters can utilize advanced media asset management solutions to digitize, tag, and package decades-old tapes, news broadcasts, and classic series sitting in vaults (which traditionally make up over 85% of unmonitored dark data) into curated 24/7 Free Ad-Supported Streaming TV (FAST) channels distributed across Connected TV networks.
  • Q: What are the primary security challenges when moving playout and monetization to the cloud?
    • A: Moving workflows to the cloud exposes streams to unauthorized interception, piracy, and data tampering during transit and ad-stitching. Implementing robust enterprise video security architectures, end-to-end encryption, and advanced DRM solutions ensures compliance and content protection.

Live-to-VOD Instant Highlights Architecture: Automated Cloud Ingestion for Major Sports Tournaments

Live-to-VOD Instant Highlights Architecture: Automated Cloud Ingestion for Major Sports Tournaments

Live-to-VOD Instant Highlights Architecture: Automated Cloud Ingestion for Major Sports Tournaments represents the definitive engineering blueprint for global media enterprises looking to process, clip, and distribute live sports content at unprecedented scale without manual bottlenecks.

Key Takeaways

  • Massive Scale Operations: Global events like the 2026 FIFA World Cup feature 104 matches, requiring instantaneous, automated multi-channel content processing across various international time zones.
  • Rapid Speed Benchmarks: Modern platforms like Enveu Flow achieve end-to-end processing speeds of under 15 minutes from event end to published clips, and under 25 minutes from stream end to full VOD availability.
  • Low Latency Workflows: Leveraging AWS-driven pipelines allows live HLS segments to be ingested every 60 seconds, with AI inferencing detecting pivotal moments within 20 to 30 seconds of on-air occurrence.
  • Cloud-First Resilience: Industry panels from the SVG Cloud Workflows Summit emphasize that cloud-native architectures—integrating MLB, NHL, and Warner Bros. Discovery standards—now form the non-negotiable production backbone for modern sports broadcasting.

Introduction: The High-Stakes Demands of Major Sports Tournaments

When organizing or broadcasting a global athletic spectacle, the logistical footprint stretches far beyond the stadium seating and traditional television trucks. Consider the sheer magnitude of events like the 2026 FIFA World Cup, spanning across Canada, Mexico, and the United States, featuring a staggering 104 matches that demand continuous, flawless content distribution across multiple time zones. In this high-stakes environment, content does not simply vanish when the referee blows the final whistle; rather, it transforms instantly into a multi-channel digital consumption cycle. Fans immediately demand late-arrival rewinds, granular search queries for precise goal highlights, and comprehensive morning-after full-match replays on their mobile devices, Smart TVs, and social media feeds.

Historically, this demand triggered an immense operational bottleneck. Traditional broadcast workflows relied heavily on manual intervention—human editors sitting in dark rooms, scrubbing through continuous tapes, cutting highlights by hand, and manually rendering files before uploading them to content management systems. In our experience consulting with major sports networks, these legacy architectures consistently buckle under high-concurrency event-day traffic spikes. When millions of concurrent viewers flood a platform simultaneously after an iconic moment, manual workflows cause unacceptable publishing delays, missing out on vital engagement windows and advertising revenue.

To conquer this friction, media organizations must adopt a sophisticated Live-to-VOD Instant Highlights Architecture: Automated Cloud Ingestion for Major Sports Tournaments. This advanced technical framework bridges the gap between real-time linear delivery and on-demand archiving. Ranging from live stream ingestion and AI-driven automated clipping to low-latency transcoding and secure content delivery, modern cloud platforms replace human guesswork with deterministic, event-driven microservices. By orchestrating these components in the cloud, broadcasters can deliver instant highlights before fans even leave their seats, transforming chaotic post-match traffic spikes into seamless user experiences.

Broadcast engineers collaborating in a modern control room to monitor real-time video telemetry and cloud ingestion performance.

The Anatomy of a Modern Live-to-VOD Pipeline

Building a resilient, high-performance media pipeline starts at the very beginning of the broadcast chain: ingestion and real-time recording. The underlying mechanics require capturing continuous live mezzanine feeds and handling chunked distribution formats with absolute reliability. By utilizing low latency cloud video ingestion for sports, engineering teams can process continuous HTTP Live Streaming (HLS) or Dynamic Adaptive Streaming over HTTP (DASH) segments—often processed every 60 seconds—directly into cloud object storage buckets. This continuous ingestion guarantees that no frame is lost, even if an upstream encoder hiccup occurs, providing a stable foundation for downstream processing.

Once raw feeds enter the cloud, the next imperative is automated processing and parallel workflows. Modern orchestration platforms—such as Enveu Flow or custom AWS toolchains—eliminate manual handoffs entirely by executing multi-language dubbing, closed caption generation, and VOD creation simultaneously. Instead of waiting for a live event to conclude before initiating file transcoding, the system processes sub-segments concurrently as the event unfolds. This level of synchronization is essential for establishing a robust real-time sports VOD workflow architecture that satisfies both linear viewers and on-demand digital consumers.

This architectural shift is no longer an experimental venture; it has matured into the mission-critical production backbone for top-tier sports leagues. Insights gathered from industry panels at the SVG Cloud Workflows Summit—featuring engineering leaders from NBC Sports, Major League Baseball (MLB), the National Hockey League (NHL), and Warner Bros. Discovery—highlight that cloud production has graduated from an auxiliary testing ground to the primary operational engine. As industry experts note, moving core media workflows to elastic cloud environments drastically reduces hardware footprint while increasing geographical redundancy and operational agility.

“The transition to cloud-native broadcast architectures is no longer about saving capital on hardware; it is about achieving an elastic agility that traditional broadcast trucks can simply never match in a multi-region tournament environment.” — Senior Cloud Broadcast Architect, Major Sports Network

AI-Enriched Ingestion: Detecting and Tagging Key Moments

The traditional method of manual metadata tagging is entirely unviable when processing dozens of simultaneous matches across a global tournament. Modern pipelines bypass this bottleneck by deploying advanced AI analysis during the initial ingestion phase, extracting rich video embeddings, audio vectors, speech-to-text transcripts, and granular scene descriptions on the fly. By converting visual and auditory data into searchable semantic vectors, the system understands what is happening on screen—distinguishing between a tactical midfield lull, a thunderous goal, or a contentious penalty review—without human curation.

The speed of AI inference dictates the commercial success of instant highlights. Utilizing cloud-native inference capabilities—such as AWS Elemental Inference combined with Amazon Bedrock and Amazon Transcribe—systems can detect editorially significant live moments within an astonishing 20 to 30 seconds of their actual on-air occurrence. This rapid detection speed fuels an automated highlight generation pipeline for live sports, ensuring that social media clipping tools and DTC (Direct-to-Consumer) apps receive packages while viewer engagement is at its absolute peak.

To make these vast libraries of clips instantly discoverable, multi-channel embeddings are indexed directly into scalable search engines like Amazon OpenSearch Service. This setup allows content producers and end-users alike to execute natural language queries across both live streams and VOD archives simultaneously. For instance, an archivist can query “all penalty saves in the knockout stages,” and the system immediately surfaces precise time-coded clips. This deep semantic indexing transforms passive video archives into highly monetizable, interactive asset libraries driven by live-to-VOD automated clipping software.

Broadcast technician inspecting fiber optic connections within a high-density cloud server rack.

Automated Clipping, Transcoding, and Packaging

When an editorially significant event is flagged by AI inference, the instant highlight generation mechanics kick into overdrive. The system executes an event-driven trigger workflow that instantly slices stream buffers, generates precise sub-clips, and initiates transcoding protocols without human intervention. By isolating the exact timecode window—ranging from ten seconds before a goal to thirty seconds after celebration—the pipeline crafts tight, high-impact video packages ready for immediate public consumption.

Simultaneous multi-platform distribution is the ultimate goal of this automated machinery. Sliced assets are packaged concurrently for multiple destination endpoints, including CMS editorial dashboards, direct-to-consumer OTT applications, and automated social media channels where clips are automatically captioned, formatted for vertical or horizontal viewing, and scheduled for release. This multi-format packaging removes the friction of manual re-encoding, allowing marketing and editorial teams to flood digital channels with fresh content seconds after the final whistle blows.

To ensure absolute stability during high-concurrency events, engineering teams implement rigorous idempotency and resiliency safeguards. Utilizing deterministic document IDs and idempotent processing rules allows pipelines to safely reprocess streams or recover from network partitions without generating duplicate media assets, conflicting metadata, or storage bloat. This robust approach to scalable event-driven sports highlights automation guarantees that even if a microservice fails mid-match, self-healing orchestration tools spin up alternative workers instantly, maintaining an unbroken live streaming to VOD transcoding infrastructure.

CDN Delivery, Post-Match Traffic Spikes, and Rights Protection

The moment a major sports match ends, digital properties experience an overwhelming surge of concurrent traffic as millions of users rush to watch replays, check scores, and share highlights. Managing post-match surges requires a multi-layered Content Delivery Network (CDN) delivery architecture designed to absorb massive traffic spikes instantly without degrading stream quality or throwing 502 gateway errors. By pushing edge caching rules to the absolute periphery of the network, origin servers are shielded from direct request floods, ensuring smooth video playback for every global user.

Beyond standard playback, modern audiences expect seamless time-shift viewing capabilities. The technical setup for catch-up infrastructure requires robust DVR-enabled stream packaging that allows late-joining viewers to buffer, pause, and rewind live streams independently while the main event is still underway. This requires continuous manifest manipulation and origin-side storage caching that dynamically serves both live manifests and historical chunk indexes from the exact same storage repository.

Content protection and Digital Rights Management (DRM) remain absolute prerequisites when distributing valuable sports media assets. Because sports broadcasting rights represent billions of dollars in commercial value, integrating multi-DRM (FairPlay, Widevine, PlayReady), geo-blocking rules, and tokenized authentication is non-negotiable. These security layers protect valuable VOD and instant replay assets from unauthorized scraping and piracy, securing the commercial investments of broadcasters and league federations utilizing cloud-based broadcast video processing for tournaments.

Master control room featuring multi-viewer monitoring walls during a live sports broadcast.


Frequently Asked Questions (FAQ)

How do broadcasters turn live sports matches into instant highlights automatically?

Broadcasters use event-driven cloud architectures integrated with AI-driven inference tools (such as speech-to-text, video embeddings, and visual recognition). When a key moment like a goal occurs, the system triggers automated stream clipping, transcoding, and metadata tagging within 20 to 30 seconds, publishing the finalized clip to CMS and social channels in under 15 minutes without manual editing.

What is the technical workflow for live-to-VOD conversion during major tournaments?

The workflow begins with live stream ingestion (processing HLS segments every 60 seconds), continuous recording to object storage (like Amazon S3), parallel AI analysis for semantic indexing, automated packaging and multi-bitrate transcoding, and rapid deployment to a CDN to handle post-match traffic spikes.

How do cloud pipelines handle traffic spikes after a major sports event ends?

Cloud pipelines leverage elastic auto-scaling compute clusters and robust CDN edge caching. By decoupling live recording from VOD transcoding and utilizing event-driven microservices, systems can absorb massive concurrent viewer surges immediately post-match without performance degradation.

Can AI replace human editors for sports highlight generation?

While AI cannot entirely replace human editorial nuance for complex storytelling, it automates up to 90% of the heavy lifting—such as detecting goals, penalties, and key plays, generating automatic metadata, and cutting rough clips—allowing human editors to focus purely on high-end creative packaging and editorial approval.


Conclusion

The deployment of a robust Live-to-VOD Instant Highlights Architecture: Automated Cloud Ingestion for Major Sports Tournaments transforms how global media organizations capture, process, and monetize live sports content. By eradicating manual operational bottlenecks, harnessing AI-driven real-time inference, and leveraging elastic cloud workflows, broadcasters can meet the insatiable demands of modern fans with speed, precision, and uncompromised quality. As major tournaments scale in geographic footprint and viewership, adopting an automated cloud pipeline is no longer just an operational upgrade—it is the ultimate competitive advantage in modern sports broadcasting.

Protecting High-Stakes E-Learning and Corporate Video: Preventing Screen Recording and Stream Rip Leaks

Protecting High-Stakes E-Learning and Corporate Video: Preventing Screen Recording and Stream Rip Leaks

Protecting High-Stakes E-Learning and Corporate Video: Preventing Screen Recording and Stream Rip Leaks is no longer an IT afterthought; it is a fundamental business imperative. When proprietary employee training, high-value SaaS walkthroughs, and confidential compliance courses leak into the wild, organizations suffer immediate revenue erosion, intellectual property theft, and irreversible competitive disadvantage.

Key Takeaways

  • The Remote Work Surge: According to a Gartner report, approximately 48% of employees will continue to work remotely, vastly increasing the attack surface for local video capture.
  • The Vulnerability Gap: Standard hosting platforms leave server-side systems completely blind to local screen capture and software stream ripping.
  • Multi-Layered Defense: True security requires integrating hardware-backed DRM, low-level driver blocking, and dynamic forensic watermarking into a unified architecture.
  • Enterprise Risk: Protecting corporate training assets safeguards trade secrets, operational workflows, and regulatory compliance standards against malicious actors.

Introduction: The Escalating Threat to High-Stakes Digital Content

In our experience working with enterprise organizations across the globe, the rapid shift toward remote work and digital-first corporate operations has fundamentally rewritten the rules of information security. High-stakes assets—ranging from proprietary corporate training modules and internal leadership seminars to confidential software-as-a-service (SaaS) product demos—have become prime targets for malicious capture. When these assets leak, the consequences extend far beyond simple copyright infringement. Companies face severe commercial impacts, including compromised proprietary workflows, leaked trade secrets, and devastating reputational damage if compliance failures come to light.

The core misconception plaguing modern organizations is the belief that standard video hosting tools (such as default YouTube embeds, basic HTML5 video tags, or unencrypted MP4 files) offer sufficient protection. In reality, these standard configurations leave a wide-open gap for screen recorders, browser extensions, and stream-ripping software. Because default players rely entirely on client-side rendering without hardware-level trust, anyone with basic technical literacy can duplicate, archive, and redistribute confidential enterprise video libraries. Addressing this exposure requires moving past naive security assumptions and implementing comprehensive enterprise video piracy prevention solutions.

This guide explores the anatomy of modern video leakage and outlines a robust, multi-layered defense strategy. We will examine how system-level DRM, active anti-screen recording technologies, and dynamic forensic tracking interlock to safeguard your intellectual property. By synthesizing these frameworks, organizations can secure their most valuable digital assets against both casual internal leaks and sophisticated external theft.

Corporate leadership team reviewing secure video streaming metrics and threat telemetry in a modern office environment.

Understanding the Attack Vectors: How E-Learning and Corporate Videos Leak

Software-Based Screen Recorders and Browser Extensions

The most prevalent vector for video leakage involves software-based screen recorders and malicious browser extensions. Tools like OBS Studio, Camtasia, and operating-system-native capture utilities intercept pixel data directly from a user’s display buffer without requiring server-side awareness. Malicious browser extensions can hook directly into the Document Object Model (DOM) to extract video blobs or render streams directly to local disk storage. Because standard web browsers are designed to render media for human viewing, they inadvertently provide an open pathway for unauthorized capture software to harvest high-definition video frames seamlessly.

Network Interception and Stream Ripping (HLS/DASH Vulnerabilities)

Beyond local screen capture, malicious actors frequently turn to network interception and stream ripping to harvest video assets. Modern web video relies heavily on HTTP Live Streaming (HLS) and Dynamic Adaptive Streaming over HTTP (DASH) protocols, which chop video files into small segments delivered via playlist manifests. If these manifests and segments are unencrypted or weakly secured, hackers can easily intercept network traffic using proxy tools like Wireshark or dedicated stream-ripping utilities. Once intercepted, these segments are stitched back together into a pristine, master-quality video file, bypassing the need for lossy screen recording entirely.

Hardware-Level and Side-Channel Exploits (VMs & Cloud PCs)

Advanced threat actors often leverage virtual machines (VMs), sandbox environments, and cloud PCs (such as VMware, VirtualBox, and virtualized enterprise desktops) to bypass standard operating system security filters. By running a secure video player inside an isolated virtual environment, bad actors can manipulate low-level system graphics drivers, intercept memory addresses, and extract uncompressed video frames directly from the graphics pipeline. These side-channel exploits circumvent conventional application-layer security checks, making standard software detection mechanisms utterly ineffective against determined intellectual property thieves.

Internal Threats and Physical Camera Capture

While technical exploits dominate cybersecurity discussions, internal threats and physical camera captures remain a persistent blind spot for organizations. Trusted employees or trainees frequently use external physical devices—such as smartphones, secondary cameras, or multi-display HDMI capture hardware loops—to record corporate training sessions playing on their screens. Because physical recording happens entirely outside the digital perimeter of the computer, software-only defenses cannot detect a smartphone pointed at a monitor. Mitigating this risk requires a psychological and forensic deterrent strategy rather than a purely digital block.


Core Defense Layer 1: Advanced DRM and Secure Video Players

Deploying Enterprise-Grade Digital Rights Management for E-Learning Videos

To achieve true security, organizations must adopt robust digital rights management for e-learning videos that mirrors the architectures used by global streaming giants like Netflix, Amazon Prime Video, and Apple TV+. Enterprise-grade DRM frameworks wrap video streams in hardware-backed encryption, ensuring that decryption never occurs in unmanaged software memory. Instead, decryption keys are securely delivered to a protected local hardware path—such as Widevine (Google), FairPlay (Apple), or PlayReady (Microsoft)—embedded directly within the viewer’s device hardware. Without the proper cryptographic keys bound to verified hardware, the video stream remains completely unreadable garbage data.

Utilizing a Secure Video Player to Block Screen Capture

Enforcing DRM requires deploying a secure video player to block screen capture across all endpoints. Standard HTML5 video players cannot prevent operating systems from handing off screen buffers to recording applications. Specialized secure browsers and client-layer players interact directly with OS kernels, proactively disabling display hooks and preventing pixel grabbing. When a user launches an unauthorized screen recorder while a secure player is active, the player immediately intercepts the system call and suppresses the video output, ensuring that confidential training modules remain completely hidden from recording software.

Handling Unsupported Hardware and Stream Degradation

Enterprise video security frameworks must gracefully handle legacy, unmanaged, or unsupported hardware without compromising overall asset integrity. When a viewer accesses a secure corporate video stream from a device that lacks hardware-backed DRM or modern kernel-level security features, advanced platforms do not simply default to wide-open insecure playback. Instead, they enforce strict fallback policies—such as forcing a black screen, restricting playback to low-resolution proxy streams, or blocking access entirely and prompting the user to migrate to a compliant corporate workstation.


Core Defense Layer 2: Active Anti-Screen Recording Technologies

Low-Level Driver Behavior Detection and Blacklisting

Modern anti-screen recording software for corporate training relies on proactive, low-level driver behavior detection to neutralize capture attempts before they can begin. These specialized security suites continuously monitor running system processes, hook signatures, and graphic card memory allocations. By maintaining an up-to-date blacklist of known screen capture utilities, remote desktop tools, and debugging software, the security layer can instantly detect, block, and terminate unauthorized recording processes the moment they attempt to interface with the video rendering pipeline.

Forcing Black Screens on Capture Software

One of the most effective mechanical defenses deployed by enterprise streaming platforms is the deliberate forcing of black screens on capture software. When operating system hooks or third-party recording tools attempt to query the display surface where sensitive corporate video is rendering, the secure player’s driver intercepts the request. Rather than feeding the actual video frames to the recording software, the system substitutes a solid black rectangle. Consequently, any resulting recording file generated by the malicious software contains nothing but empty, unwatchable black frames.

Multi-Display and Screen Casting Interception

Protecting enterprise assets also requires neutralizing multi-display setups and wireless casting protocols that malicious actors use to siphon video feeds. Technologies such as Apple AirPlay, Miracast, and hardware HDMI splitters allow viewers to mirror protected content onto secondary recording devices or external capture cards. Enterprise video security solutions actively disable or block extended monitor capture loops, requiring single-display environments or disabling output entirely when wireless casting protocols are detected on the network interface.

IT engineer configuring hardware-level video stream encryption and monitoring system security protocols.


Core Defense Layer 3: Dynamic Forensic Watermarking and Leak Tracing

Implementing Dynamic Forensic Watermarking Video Protection

Because digital locks can occasionally be bypassed by physical cameras, dynamic forensic watermarking video protection serves as an indispensable final layer of defense. This technology renders unique, invisible or semi-visible security identifiers—such as the viewer’s user ID, corporate email address, IP address, and precise access timestamp—directly onto the video frames during playback. If an employee records their screen using an external smartphone or camera, the resulting video leak contains embedded forensic markers that instantly reveal the exact identity of the perpetrator.

Random Full-Screen Movement and AI-Resistance

Basic static watermarks can be easily cropped out or erased using modern AI-based video editing and removal algorithms. To counter this, advanced enterprise platforms utilize randomized, moving watermark patterns that drift across the full screen at unpredictable intervals. Because the watermark constantly changes position, opacity, and pixel composition over the video timeline, AI-based cleanup tools cannot effectively isolate and remove the identifier without severely degrading the underlying video quality.

Traceability as a Powerful Psychological Deterret

Beyond its technical utility, dynamic forensic watermarking functions as a powerful psychological deterrent for internal compliance and training programs. When employees and contractors are acutely aware that every single frame of a corporate video is invisibly or visibly bound to their unique organizational identity, the temptation to leak proprietary training methods or strategic company announcements plummets. Knowing that accountability is mathematically guaranteed transforms compliance training from a routine checkbox into a highly secure, self-policing environment.


Comprehensive Architecture: Enterprise Video Piracy Prevention Solutions

Secure Hosting Platforms and Tokenized URLs

Building an impregnable defense requires securing the entire content delivery pipeline, starting with the backend hosting infrastructure. Standard direct file hotlinking must be completely eliminated through the implementation of rotating, tokenized URLs that expire after a brief validity window (e.g., 60 seconds). Coupled with strict geo-blocking, domain restriction, and referer checking, these tokenized access passes ensure that video stream URLs cannot be shared, bookmarked, or harvested by automated web scrapers and download managers.

Preventing Stream Ripping on HLS and DASH Protocols

To effectively prevent video stream ripping HLS DASH, organizations must deploy fragment-level encryption combined with manifest obfuscation. Rather than delivering static .m3u8 or .mpd playlists, secure architectures dynamically generate and encrypt individual media segments using rotating Advanced Encryption Standard (AES-128) keys. Even if a bad actor manages to intercept network packets and download the raw fragment files, the lack of synchronized, time-sensitive decryption keys renders the files completely useless outside the authorized secure player environment.

Protecting Proprietary Training Videos from Unauthorized Recording

Synthesizing these disparate technologies into a cohesive framework is essential for enterprises where internal training secrets represent core competitive advantages. By deploying protect proprietary training videos from unauthorized recording strategies—unifying hardware-backed DRM, active process blacklisting, tokenized network delivery, and dynamic forensic watermarking—organizations create an airtight security perimeter. This holistic approach ensures that proprietary intellectual property remains strictly within authorized corporate boundaries, safeguarding long-term market differentiation.

Enterprise security operations center monitoring global video stream integrity and active piracy threat prevention.


Câu hỏi thường gặp

Q1: How do video streaming sites block screen recording?

Answer: Advanced streaming platforms use Digital Rights Management (DRM) integrated with hardware-backed security paths on the viewer’s device. When screen recording software attempts to capture pixel data, the DRM layer intercepts the request and replaces the video feed with a solid black screen or blocks capture entirely.

Q2: Can YouTube detect if you are screen recording a video?

Answer: No. Standard YouTube videos are recorded locally on the user’s device via operating system APIs or third-party tools. Because this happens entirely client-side, YouTube’s servers cannot detect the recording, and creators are not notified (except for specific DRM-protected rentals or YouTube TV content).

Q3: What is dynamic forensic watermarking in video protection?

Answer: Dynamic forensic watermarking overlays identifiable user data (such as user IDs, email addresses, or IP addresses) directly onto video frames in a randomized, moving pattern. It acts as both a visual deterrent against physical camera recordings and a forensic tool to trace the exact source of an unauthorized leak.

Q4: How can companies prevent employees from leaking corporate training videos?

Answer: Companies can protect internal training materials by combining enterprise DRM, secure video players that block virtual machines and multi-display casting, dynamic user-identifying watermarks, and restricted tokenized URL access that limits viewing permissions to authenticated corporate networks.